

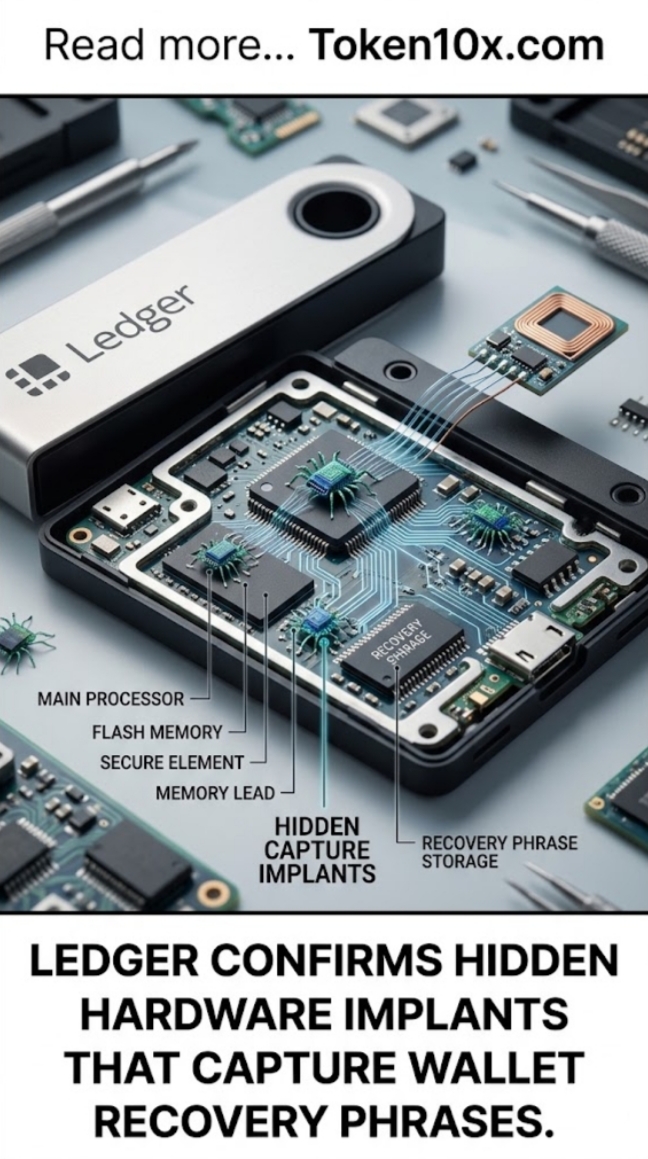
Ledger has confirmed the presence of unauthorized hardware implants in at least one affected customer’s device. As of mid-October 2026, the company verified that a wallet sold through Southeast Asian reseller CryptoBilis contained a hidden electronic component. Independent researchers have described similar modifications designed to intercept the 24-word recovery phrase during device setup and transmit it remotely. On-chain estimates place related losses in the tens of millions of dollars across hundreds of wallets.
The discovery continues to drive a formal investigation. It has restricted confirmed cases so far to devices linked to the specific reseller. Existing analysis focuses on physical supply-chain tampering rather than a compromise of Ledger’s own systems or secure element. Users and security researchers rely partly on teardown reports while routing recovery guidance through official company advice. This highlights the difference between software or phishing attacks and sophisticated hardware-level interception.
The Drivers of the Current Situation
The main issue is the insertion of hidden circuitry into hardware wallets before they reached end users. Ledger confirmed an unauthorized implant in one impacted device. Researchers examining modified Ledger Nano X units found additional components that monitor signals sent to the display. During initial setup, when the recovery phrase appears on screen, the implant can reconstruct the words and send them via a cellular modem equipped with an eSIM.
Detection has limited the immediate scope. Some versions of the implant were designed to sit beneath the screen while preserving the original battery and overall appearance. Ledger’s Genuine Check verifies the secure element but may not detect added external circuitry. Only devices purchased through CryptoBilis have been publicly tied to the confirmed cases. Broader estimates of drained funds remain unverified by the company itself.
Continued investigation requires examination of additional devices and supply-chain records. Limited public technical details on every implant variant form a narrower path at present. Ledger, researchers, and affected users are actively addressing the findings. The situation is a confirmed physical tampering incident tied to recovery-phrase interception.
Impact and Broader Context
Questions about Ledger revealing how hidden chips stole wallet recovery keys keep growing. The confirmation creates uncertainty around the full number of affected devices and the total scale of losses. It also raises broader concerns about hardware-wallet supply-chain security. Manufacturers, resellers, and users continue to assess the implications.
The issue drives debate on the residual risks of even “air-gapped” hardware wallets. It raises questions about how recovery phrases are displayed, the limits of current authenticity checks, risks associated with third-party resellers, effects on user confidence in hardware storage, and competition between official sales channels and secondary markets. Stakeholders stress that the implant targets the setup process rather than the secure chip itself. Official guidance advises against initializing recent CryptoBilis devices and recommends transferring assets to wallets created with entirely new recovery phrases on trusted hardware.
The mid-October confirmation forced formal acknowledgment of the hardware implant. The current investigation shows how further device analysis, law-enforcement involvement, and any additional findings will determine the full scope of the incident.
New confirmations of additional implants, updated loss figures, or enhanced anti-tampering measures will clarify the extent of the compromise and the protective steps available to users.
This analysis uses Ledger’s public statements, independent hardware teardowns, and contemporaneous reporting. The exact number of affected devices, total losses, and full technical details remain subject to the ongoing investigation.