

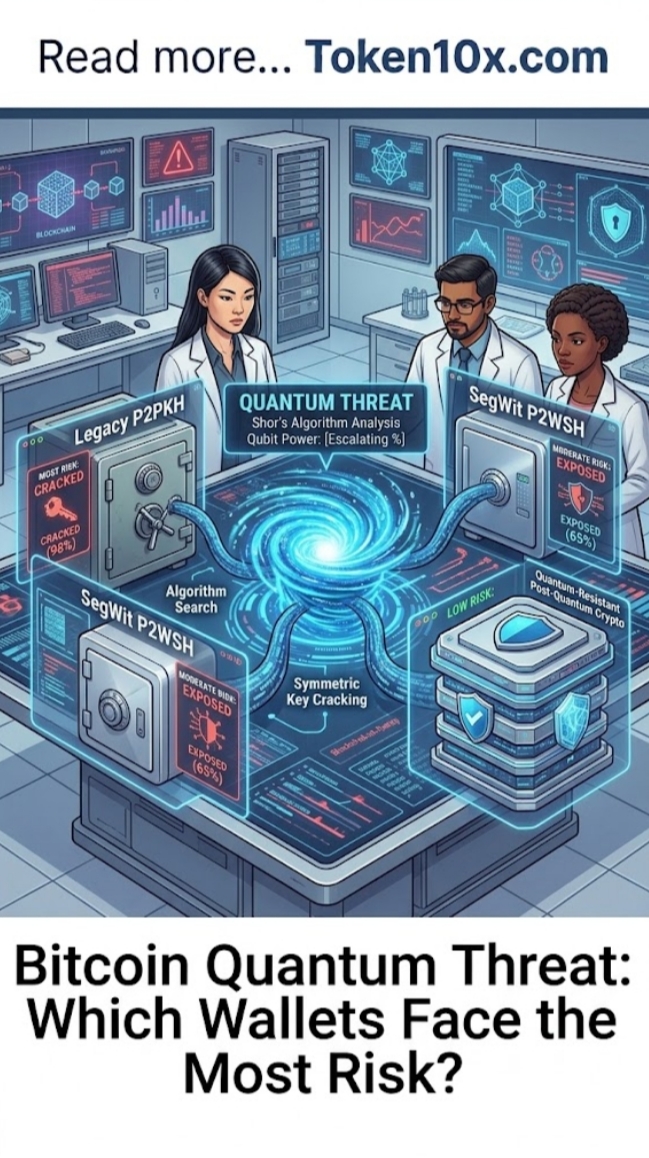
Discussions of quantum computing risks to Bitcoin continue to focus on wallet-level exposure rather than the protocol itself. As of late 2026, estimates indicate that roughly 6 to 7 million BTC—about 30 percent of the circulating supply—sit in addresses where the public key has already been revealed on-chain. No quantum computer capable of breaking Bitcoin’s elliptic-curve cryptography currently exists. The concern centers on a future machine powerful enough to run Shor’s algorithm against exposed keys.
The network continues operating under existing signature schemes. It has restricted immediate practical risk to addresses with visible public keys. Existing hash-based protections for unspent outputs remain intact for many holdings. Analysts rely partly on on-chain scans of address types while routing assessments through the distinction between exposed and unexposed keys. This highlights the difference between theoretical long-term threats and the current absence of capable hardware.
The Drivers of the Current Situation
The main issue is public-key exposure. Once a public key appears on-chain, a sufficiently advanced quantum computer could theoretically derive the corresponding private key and spend the funds. Legacy Pay-to-Public-Key (P2PK) outputs reveal the full public key from the moment they are created; these include many early coins and account for an estimated 1.7 million BTC. Address reuse across other formats (P2PKH, SegWit, and certain Taproot spends) reveals the key on the first outgoing transaction, after which any remaining or returned balance inherits the exposure. This reused-address category forms the larger share of the vulnerable total.
Holders have limited options once a key is exposed. Some institutional and exchange wallets show elevated reuse rates according to analytics firms. Fresh addresses that have never been spent from publish only a hash and therefore remain protected against this specific attack vector for the time being. Europol and other reports emphasize that the blockchain’s consensus and hashing functions are comparatively resilient, while wallets constitute the primary point of exposure. Only migration of funds to new, unused addresses (or eventual post-quantum schemes) can reduce the risk for currently exposed coins. Broader timelines for fault-tolerant quantum machines remain uncertain and subject to ongoing hardware progress.
Continued safety for unexposed holdings requires avoiding address reuse. Limited migration tools under present standards form a narrower path. Researchers and wallet providers are actively tracking exposure metrics. The situation is a long-horizon cryptographic challenge tied to key visibility.
Impact and Broader Context
Questions about the Bitcoin quantum threat and which wallets face the most risk keep growing. The concentration of exposure in reused and legacy addresses creates uncertainty around the scale of any future disruption. It also affects custody practices at exchanges and among long-term holders. Cryptographers, exchanges, and protocol developers continue to examine mitigation pathways.
The issue drives debate on quantum readiness. It raises questions about how quickly post-quantum signature schemes can be standardized and adopted, the limits of migrating large volumes of exposed coins, risks to dormant or lost early wallets, effects on exchange cold-storage practices, and competition between different address-type risk profiles. Stakeholders stress that no immediate attack capability exists. Reports say the highest-risk wallets are those with already-visible public keys—particularly P2PK outputs and any address that has been spent from—while never-used hashed addresses remain comparatively safer for now.
Recent analyses and agency reports forced renewed attention onto the distribution of exposed supply. The current cryptographic review shows how hardware progress and any protocol upgrades will determine the practical timeline.
New exposure statistics, wallet-migration tools, or advances in quantum hardware will clarify the relative risk across different Bitcoin holdings.
This analysis uses on-chain estimates from analytics firms, advisory reports, and recent assessments by agencies such as Europol. Risk timelines and exposure figures remain subject to ongoing research and technological developments.