

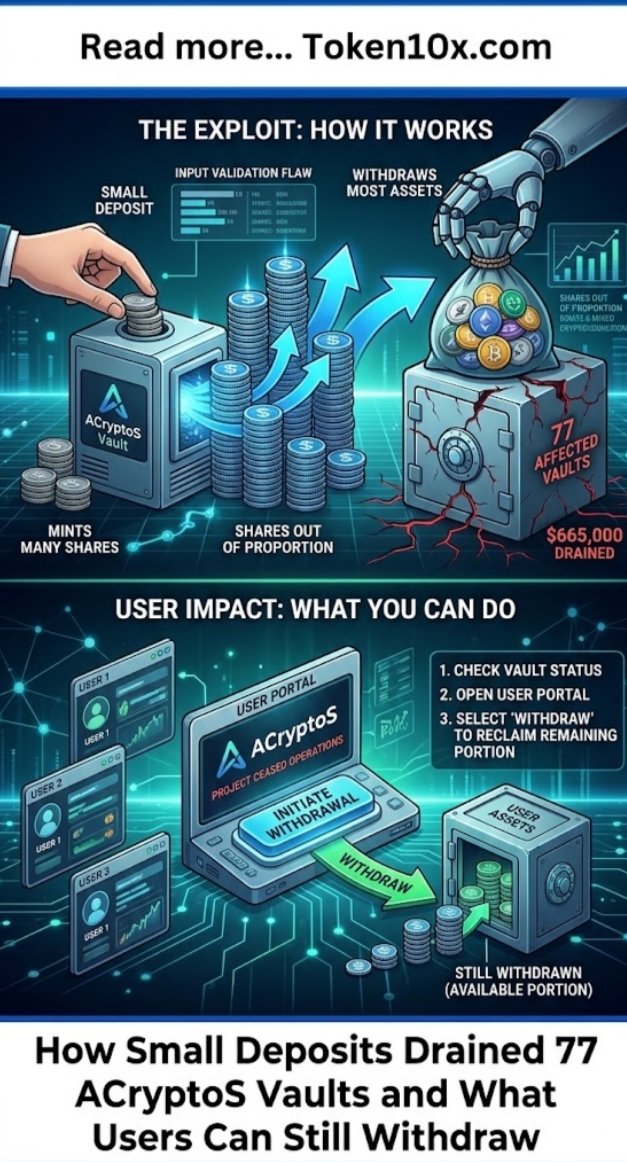
ACryptoS, a DeFi yield aggregator specializing in concentrated-liquidity vaults, suffered an exploit on November 8, 2026, that drained approximately $665,000 across 77 vaults on five EVM chains. Attackers exploited a missing input-array length check in the depositMulti function. By supplying a single-token amounts array shorter than the vault’s token count, they caused the contract to price its own holdings using only token0. A minimal deposit of one token then minted the vast majority of the vault’s shares—often around 90 percent—allowing an immediate withdrawMulti to extract a pro-rata share of both tokens.
The attack ran from roughly 02:02 to 16:22 UTC and involved 135 addresses. Losses broke down as approximately $230,000 on Arbitrum (28 vaults), $191,000 on BSC (12 vaults), $135,000 on Polygon (11 vaults), $70,000 on Base (13 vaults) and $40,000 on Optimism (13 vaults). ACryptoS confirmed the bug, disabled deposits across all affected vaults by 16:40 UTC, left withdrawals open, offered the attacker a 10 percent bounty for returned funds, and announced that the project is being deprecated with no plans to reopen deposits. Users are urged to withdraw remaining assets immediately.
The Drivers of the Current Situation
The main issue is a straightforward input-validation failure in the multi-token deposit path of UniV3-family vaults (Uniswap V3, SushiSwap V3, PancakeSwap V3 and Biswap V3). Because the contract never verified that the length of the _amounts array matched the number of tokens, a one-element array caused the valuation logic to ignore every token except the first. A tiny deposit of that single token therefore received a disproportionately large share of the vault’s total supply, which could then be redeemed for most of the multi-asset reserves.
Related factors shaped the outcome. The vulnerability had existed undetected; once triggered, it was repeated efficiently across dozens of relatively small pools. Only the official post-mortem, the confirmed $665,000 loss figure, the five-chain impact, the precise depositMulti length-check failure, the continued availability of withdrawals, and the decision to deprecate the protocol are confirmed. Broader DeFi practices around multi-asset vault accounting and the speed of cross-chain fund movement after the exploit contributed to the final scale.
Continued monitoring requires observation of residual balances in the 77 vaults, any voluntary returns under the bounty offer, and user withdrawal activity while the function remains live. Limited remaining liquidity in some pools and the permanent closure of deposits form a narrower path for recovery. ACryptoS and on-chain analysts remain the primary parties documenting residual effects. The situation is a classic input-validation exploit that has left withdrawals intact but permanently ended the protocol’s operations.
Impact and Broader Context
Questions about remaining user funds keep growing. The exploit creates uncertainty about how much value is still recoverable from the drained vaults and about the practical window for withdrawals before any further issues arise. It also elevates attention on the risks of unvalidated multi-token deposit interfaces in concentrated-liquidity designs. Depositors, security researchers and other yield aggregators continue to assess the implications.
The issue drives debate on input-validation standards for multi-asset vaults. It raises questions about the durability of share-minting logic when array lengths are not enforced, the limits of post-exploit mitigation when a project elects to shut down, risks of similar length-check omissions in other UniV3-style contracts, effects on near-term confidence in smaller DeFi yield platforms, and competition among audited versus lightly maintained aggregators. Coverage notes that ACryptoS has kept withdrawals open and advised users to act promptly while funds remain accessible.
The November 8 exploit and subsequent post-mortem forced renewed focus on vault accounting hygiene. The current status shows how residual balances, any bounty returns, or further on-chain activity will determine the lasting effect for affected users.
New balance snapshots, confirmed withdrawal success rates, or additional technical disclosures will clarify how much value users can still recover.
This analysis uses ACryptoS’s official post-mortem and contemporaneous reporting. The ultimate recovery of remaining funds and any partial restitution remain subject to user action and the attacker’s response to the bounty offer.