

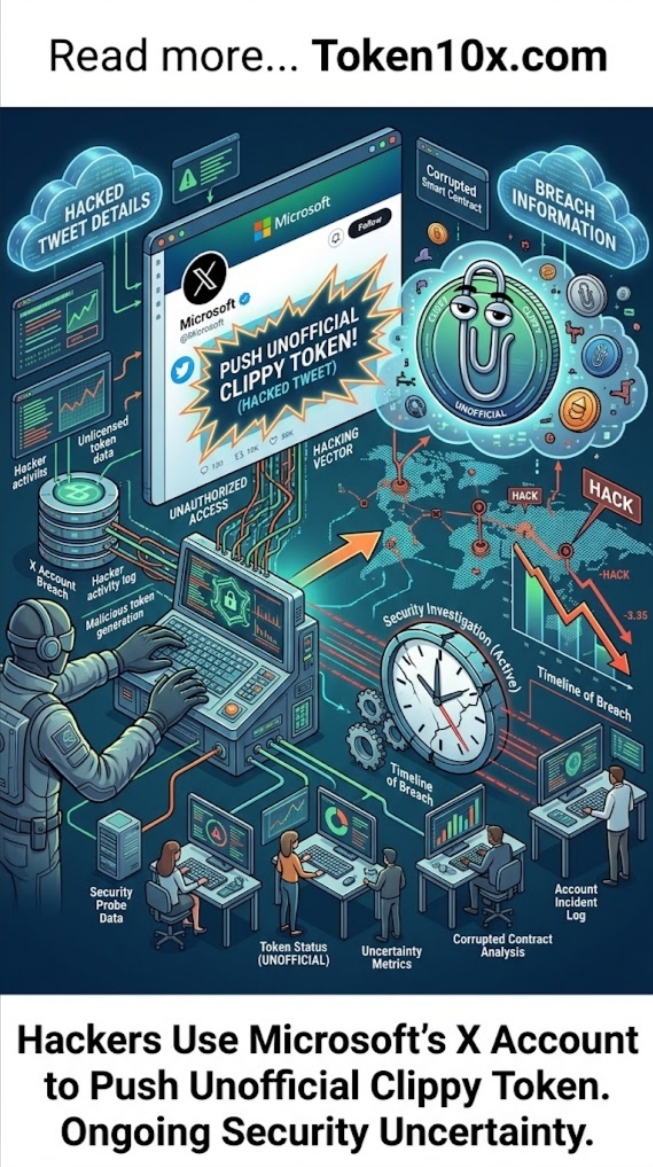
Hackers compromised Microsoft’s official X account to promote an unauthorized Clippy-themed cryptocurrency token. As of early October 2026, the account with more than 13 million followers was briefly controlled on October 1–2. Attackers changed the profile picture, followed a promotional account, and reposted content linking Clippy to the unofficial token. Microsoft regained control within roughly 30 minutes and removed the posts.
The company continues to secure the account and investigate the breach. It has restricted further unauthorized activity and issued clear denials of any connection. The token remains live on decentralized platforms. Microsoft relies on platform recovery tools and legal measures while routing communications through official channels. This highlights the difference between rapid account recovery and the lasting exposure created by the short-lived promotion.
The Drivers of the Current Situation
The main issue is the temporary takeover of Microsoft’s verified X account for crypto promotion. Attackers used the account to interact with a Clippy-impersonating profile and amplify a call for likes to “bring Clippy back,” directing attention to the unofficial CLIPPY or $Clippy token. No internal Microsoft systems beyond the social-media account appear to have been affected. The promotional activity was removed after the account was secured.
Microsoft has limited the visible damage by deleting the posts and changing the profile image back. Some related promoter accounts were suspended. The company points to the unauthorized nature of the access and states it has not authorized, sponsored, or endorsed any cryptocurrency linked to Clippy, Microsoft, or the $MSFT ticker. Promoters of the token claimed liquidity pools and, in some cases, false associations with Microsoft shares. Investigators and the company are reviewing how access was obtained. Only the short window of control allowed the message to reach a large audience. The token itself continues trading independently.
A complete resolution requires successful legal removal of the token materials and full forensic closure. Limited public exposure under quick recovery is a narrower path. Security teams and platform moderators are actively examining the incident. The situation is a social-media security challenge tied to the high-visibility account compromise.
Impact and Broader Context
Questions about hackers using Microsoft’s X account to push an unofficial Clippy token keep growing. Brief verified-account abuse creates uncertainty for brand integrity and user trust. It also affects the visibility of the unauthorized token. Microsoft, X, and blockchain monitors continue to track residual promotion and any related trading activity.
The issue drives debate on social-platform security for major brands. It raises questions about how quickly verified accounts can be weaponized for crypto schemes, the limits of platform recovery tools, risks of meme-character exploitation, effects on investor confusion around official versus unofficial tokens, and competition between rapid response and lasting scam amplification. Stakeholders stress that the unauthorized posts do not represent Microsoft. The company says it is investigating the circumstances, has secured the account, and will pursue legal action to remove the token and related materials.
The October compromise forced a high-profile brand into an immediate damage-control process. The current investigation shows how short-duration account takeovers will be handled in the current social-media environment.
New forensic findings, legal actions, or token-market developments will clarify the full impact of the Clippy-token promotion.
This analysis uses Microsoft statements, platform reports, and related coverage. Account status and residual token activity remain subject to ongoing investigation and possible further measures.