

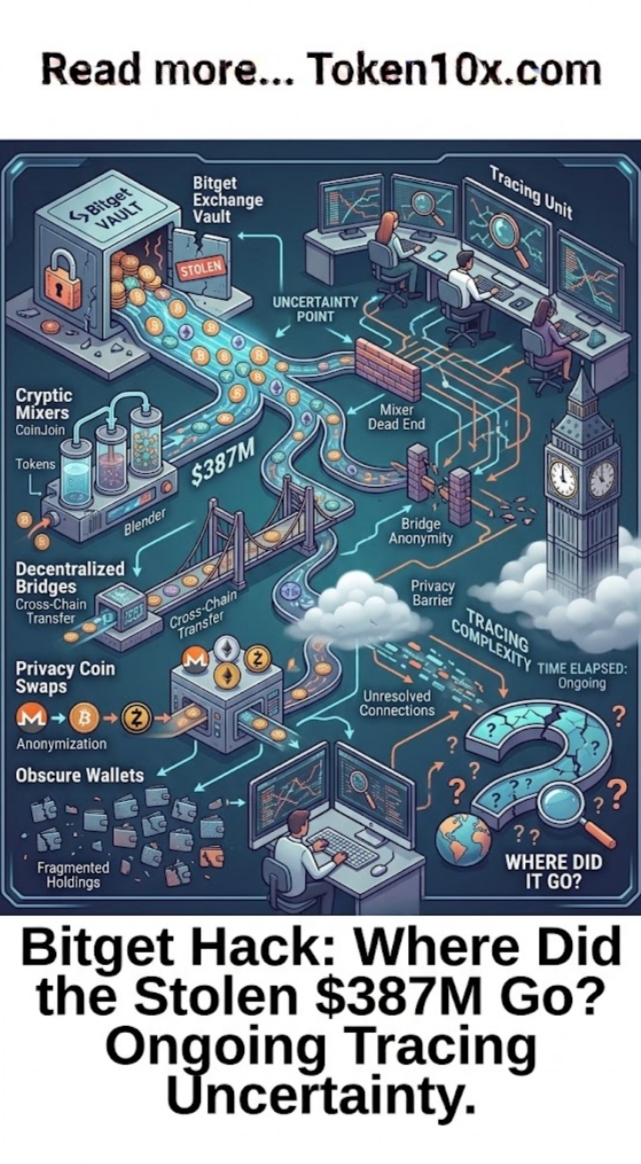
Bitget suffered a major security breach involving approximately $387.5 million. As of early October 2026, the exchange confirmed unauthorized transfers from hot and warm wallets on September 24. Cold wallets remained unaffected. Private keys were not compromised. The loss falls within the coverage of Bitget’s User Protection Fund. Most of the stolen assets have been moved and partially laundered.
The attacker continues to control the bulk of the funds. Investigators have traced movements across multiple blockchains. Freezable assets were rapidly converted. Significant value has consolidated into Bitcoin. Only a small fraction has been frozen. Bitget relies on on-chain analytics firms, law enforcement, and its protection fund. This highlights the difference between rapid detection and the slower process of recovery.
The Drivers of the Current Situation
The main issue is the successful theft and subsequent dispersal of roughly $387.5 million. The attacker compromised a critical backend system in Bitget’s wallet infrastructure and spoofed transaction data to trigger authorized transfers. The figure rose from an initial $351.6 million after additional Zcash and Tron assets were accounted for. No further unauthorized outflows have occurred.
Funds left across multiple chains in rapid bursts. XRP formed the largest single portion, followed by Ethereum-based assets and others. The attacker quickly swapped freezable tokens such as USDT and USDC. Cross-chain protocols including THORChain handled substantial pass-through volume into Bitcoin. Some proceeds entered CoinJoin transactions or privacy pools. North Korean-linked groups remain the primary suspicion based on operational patterns. Only a limited amount—around $840,000 to $1.1 million—has been publicly frozen by issuers. The majority stays under attacker control in monitored but unrecovered wallets.
Full recovery requires successful tracing, freezes, or seizures. Limited freezes under active laundering form a narrower path. Blockchain investigators and law enforcement are actively examining the routes. The situation is a recovery challenge tied to sophisticated cross-chain obfuscation.
Impact and Broader Context
Questions about where the stolen $387 million from the Bitget hack went keep growing. Dispersed and laundered funds create uncertainty for recovery prospects. They also affect confidence in exchange hot-wallet security. Analytics firms such as Chainalysis, BlockSec, and others, along with Bitget’s partners, continue to track the assets.
The issue drives debate on exchange infrastructure risks. It raises questions about how effectively backend controls prevent spoofed authorizations, the limits of cross-chain monitoring, risks of privacy tools in laundering, effects on user protection funds, and competition between rapid response and long-term asset recovery. Stakeholders stress that early freezes capture only a fraction of proceeds. Bitget says it is cooperating with investigators, has replenished its protection fund, and does not expect to recover a large share of the stolen assets.
The September 24 incident forced one of the larger exchanges into an intensive tracing effort. The current on-chain review shows how post-theft fund movements will determine ultimate recovery outcomes.
New freezes, seizures, or investigator updates will clarify the final disposition of the stolen $387 million.
This analysis uses Bitget statements, on-chain reports from Bitquery, BlockSec, Chainalysis, and related coverage. Fund locations and recovery prospects remain subject to ongoing investigation and possible enforcement.