

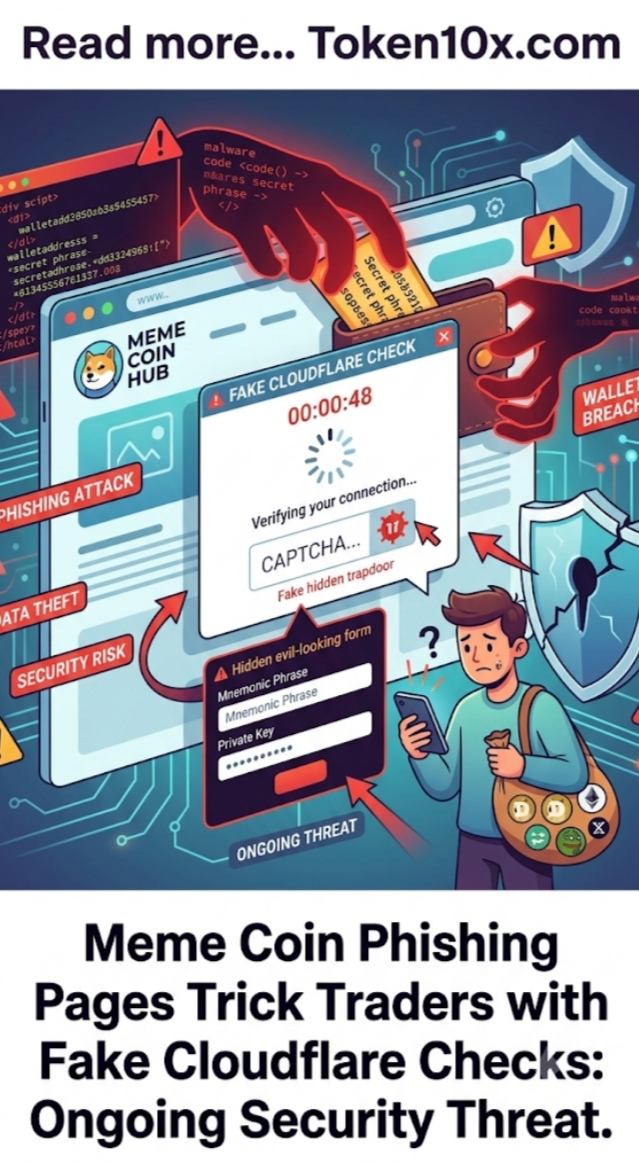
Meme coin traders continue to face an extraordinary risk from sophisticated phishing campaigns, with attackers deploying pages that mimic legitimate Cloudflare verification screens and leading to substantial losses exceeding hundreds of thousands of dollars for individual victims. As of September 16, 2026, reports confirm that multiple popular meme coin display pages have redirected users to these fake checks, following incidents where one prominent trader lost approximately $600,000 after executing a malicious script.
The scam still surpasses many conventional wallet-drainer tactics in its directness and potential impact. One successful attack can drain an entire computer’s crypto holdings, representing far more than typical single-transaction losses in the meme coin sector where rapid launches and research clicks are common. This comparison underscores the immense scale of social engineering risks generated by token metadata vulnerabilities in today’s high-volume on-chain trading environment.
The Drivers of This Enduring Phishing Threat
The key factor remains the placement of malicious links in meme coin token metadata fields, such as official website or social media URLs displayed on platforms like DexScreener. Attackers update these fields—often controllable by creators or claimed “community takeovers”—to point to phishing sites that present a convincing fake Cloudflare “verify you’re human” screen. Users are then instructed to run an administrator-level payload script on Windows, which installs malware capable of draining wallets and broader system access. This stacks with the speed of meme coin launches and trader habits of quickly researching new tokens amid recent market activity.
For perspective, the tactic has already claimed at least one high-profile loss of around $600,000 from trader @cladzsol, with warnings circulating from accounts like @insidecalls highlighting multiple affected pages. Only the most cautious traders who immediately close suspicious verification prompts avoid exposure. Smaller or less vigilant participants across Solana and other chains sit below this level of protection when following on-screen instructions.
It is essential to distinguish: legitimate Cloudflare checks never require users to execute system commands or scripts, whereas these phishing pages capture full device control rather than isolated wallet approvals. The threat is mostly malware-based and linked to the open nature of token metadata addressing the need for project discovery in decentralized markets.
The Impact and Broader Context
Emerging alongside the meme coin boom, these phishing pages have transformed routine research into high-stakes risks. Platforms display metadata links without rigorous real-time verification. Attackers introduced fake Cloudflare interstitials that bypass typical blockchain transaction prompts, cut reliance on wallet connections, and grow the potential for complete PC-level compromises. Security observers pursue greater awareness to counter such evolving social engineering.
This sustained activity fuels debates on platform responsibility, user education, and metadata safeguards. Advocates highlight the need for better screening on aggregators, immediate closure of suspicious pages, and ambitions for safer research tools. Critics raise concerns over delayed reviews and suggest measures like stricter field controls or automated warnings.
Security analysts note that metadata-driven phishing stems from scalable token creation and high-risk speculative trading. Experts have stressed prioritizing caution over curiosity, with benefits flowing to the community via shared alerts and improved hygiene practices.
As developments in meme coins, on-chain discovery tools, and phishing techniques unfold, these incidents offer insight into modern crypto security dynamics. Platform responses and trader vigilance will shape both individual outcomes and broader market resilience.
This analysis draws from real-time market reports, trader disclosures, and security warnings for precision. Figures remain subject to ongoing incident updates.